After an acquisition closes, two groups of people need to work together right away, and each group signs in to its own Microsoft environment. Mailboxes, files and Teams can move later. Identity has to be handled first, because every other workload depends on it: who can sign in, what they can reach, and which security policies apply to them.
This guide covers the identity decisions to make before and after close, how to give both companies access to each other on day one without a rushed migration, and how to sequence the move to a single tenant. If you are planning the full tenant-to-tenant move, our Microsoft 365 tenant migration planning guide covers workloads, domains and cutover.
Start with the end state
Before anyone changes a setting, decide what the combined company should look like in a year. There are three common end states:
- One tenant. The acquired company’s users, devices and data move into the acquirer’s Microsoft 365 and Entra ID tenant. This is the usual goal when the businesses will operate as one.
- Two tenants, connected. Both tenants stay, with cross-tenant access configured so people can collaborate. This fits a business that will keep operating separately, or one that may be sold again.
- Two tenants for now, one later. Connect the tenants for the integration period, then consolidate once the business is ready. Most mid-market acquisitions land here.
The end state determines how much effort to put into the interim setup. If the tenants will be connected for two years, the interim configuration deserves the same care as a permanent one.
Decisions to make before close
Some identity questions can be answered during due diligence, and answering them early prevents surprises in the first week.
Who controls the acquired tenant today? List every account with Global Administrator or other privileged roles in the acquired company’s tenant, including outside providers. On day one, the acquirer needs at least one verified administrator in that tenant, and every other privileged account should be reviewed.
Is the acquired company cloud-only or hybrid? If the company syncs accounts from an on-premises Active Directory, identity changes have to be planned in both places. A hybrid environment adds steps and makes the timeline longer.
What security baseline does the acquired tenant meet? Compare multifactor authentication coverage, Conditional Access policies, legacy authentication settings and device compliance rules against your own standard. Gaps here become your risk as soon as the networks and tenants are connected.
Are there service agreements that limit changes? In a carve-out, the seller may run some IT services under a transition services agreement for a set period. That agreement can limit when you can move identities and who must approve changes.
What licenses come with the business? Licensing differs between tenants, and some features you rely on, such as Conditional Access or identity protection, depend on the license tier. Know what each user will have during the interim period.
Day one: give people access without moving them
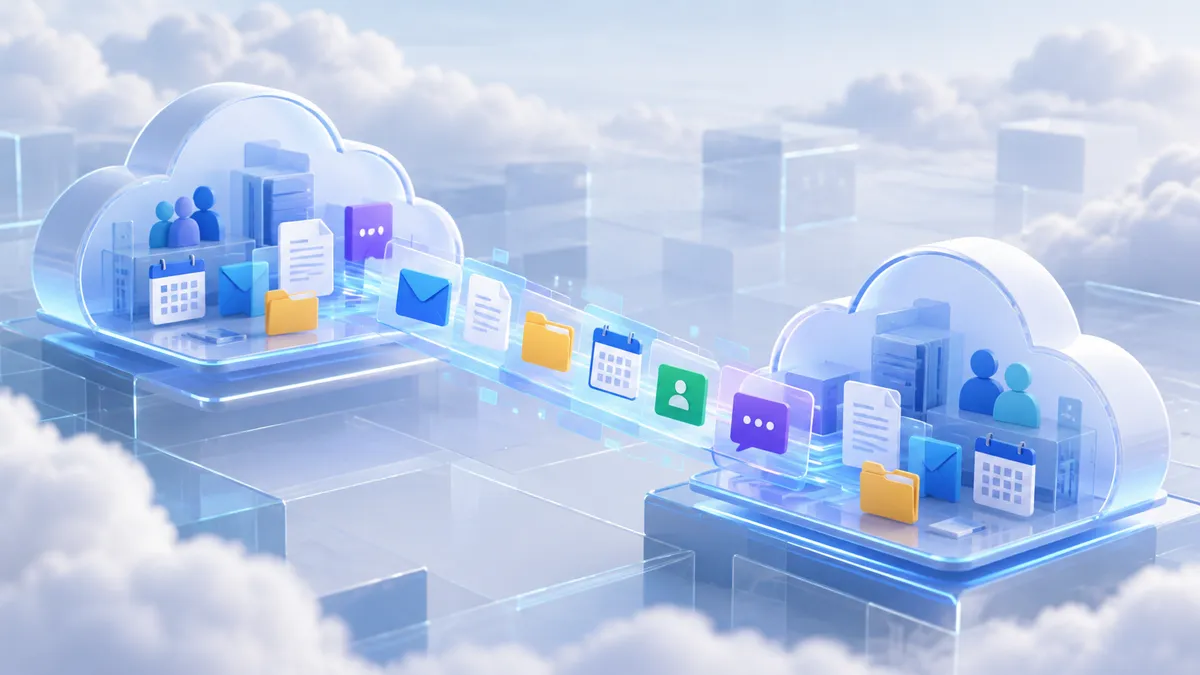
The goal for day one is simple: people in both companies can find each other, meet, and share files, with security controls you trust. That does not require migrating anyone.
Microsoft Entra ID offers several ways to connect two tenants:
- B2B collaboration. Users from one tenant are invited into the other as guests. This works for a small number of people who need access to specific resources.
- Cross-tenant access settings. These control which users and groups can collaborate across the two tenants, and whether one tenant trusts the other’s multifactor authentication and device compliance signals. Setting these deliberately avoids prompting users twice and avoids trusting a tenant whose controls you have not reviewed.
- Cross-tenant synchronization. This automatically creates, updates and removes accounts for selected users from one tenant in the other, so you are not inviting people one by one. It is the usual choice when many people need access.
- Multitenant organization features in Microsoft 365. These help people find and work with colleagues across the connected tenants in Teams and other Microsoft 365 apps, once synced users are set up as members in each tenant.
Feature names and licensing requirements for these options change, so confirm the current requirements with Microsoft documentation or your partner before you commit to a design.
Whichever option you choose, decide which groups get access and in which direction. A common mistake is to open full access both ways on day one and then struggle to narrow it later.
Secure the acquired environment early
The weeks after close are a period of elevated risk. Attackers watch for acquisition announcements, and staff are expecting unfamiliar emails from new colleagues and new IT contacts. Prioritize these steps in the first weeks:
- Confirm who holds administrator roles in the acquired tenant, and remove or reduce access that is no longer needed.
- Enforce multifactor authentication for all users, starting with administrators.
- Block legacy authentication protocols if they are still enabled.
- Review accounts for people who have left the company, shared mailboxes with sign-in enabled, and service accounts with broad permissions.
- Tell employees in both companies how IT will contact them during the integration, so they can recognize impersonation attempts.
Sequence the move to one tenant
If the end state is a single tenant, sequence the consolidation so identity leads and workloads follow.
- Inventory. List users, groups, devices, applications that use Entra ID for sign-in, and any on-premises directory dependencies.
- Map identities. Decide how each acquired user will appear in the combined tenant: username format, email address, group memberships and licenses. Agree on how to handle people who already have accounts in both tenants.
- Prepare the target tenant. Create groups, licensing assignments and Conditional Access policies for the incoming users before they arrive.
- Migrate in batches. Move users and their data in planned groups. Each batch is a point where you can check sign-in, access and mail flow before continuing.
- Move the domain last. A custom domain can be verified in only one tenant at a time, so it is usually moved at the end, once the users who depend on it have moved.
- Decommission. Remove cross-tenant access that is no longer needed, retire the old tenant according to your retention requirements, and close remaining administrator accounts.
Common mistakes
- Treating identity as part of the email migration. Mailbox moves get the attention, and identity decisions get made in a hurry along the way.
- Trusting the acquired tenant’s security signals without review. Cross-tenant trust settings can accept the other tenant’s MFA and device compliance. That is only safe after you have checked those controls.
- Leaving interim access in place indefinitely. Connections set up for the integration period should have an owner and an end date.
- Ignoring applications. Business applications that use Entra ID for sign-in need to be reconfigured, and they are easy to miss in the inventory.
How Virteva helps
Virteva holds Microsoft’s Identity and Access Management specialization and works with mid-market organizations on Microsoft identity and security. For acquisitions, that includes reviewing the acquired environment, designing the interim cross-tenant setup, and planning the consolidation. Read more about Microsoft identity and security services and IT advisory services.
Frequently asked questions
Do we have to migrate the acquired company right away? No. Most organizations connect the two tenants for collaboration first and consolidate later, once the business decisions are settled. Moving too quickly can disrupt the acquired team during an already busy period.
How long does identity consolidation take? It depends on the number of users, whether the acquired company uses an on-premises directory, how many applications rely on Entra ID for sign-in, and any agreements with the seller. Building the inventory first is the most reliable way to estimate the timeline.
Can the acquired company keep its email domain? Yes. The domain can be added to the combined tenant once it is removed from the original one, so users can keep their addresses. Plan the domain move for the end of the migration.
Next step
If you are planning an acquisition or have just closed one, talk to Virteva about the identity decisions above before the integration timeline is set.